
Identified vulnerabilities
0+Why they trust us
We help businesses build reliable cyber protection and maintain its operations. We approach each project individually — we take into account the specifics of the business, inspection objects, access limits, and the level of involvement.

Infrastructure is our profile
We build networks and servers from scratch, so we understand not only how to hack, but also how to do it right

International standards
We work according to OWASP, PTES, NIST and CIS methodologies.

Actionable documentation
Each project is accompanied by working documents: reports, schemes, regulations, instructions

Confidentiality by NDA
No project information leaves the agreed scope. Confidentiality is established from day one
Services
Key cybersecurity services
From finding vulnerabilities to incident response and building a security system
Network and server infrastructure protection
- We are opening a new office
- The infrastructure has grown
- We are preparing for certification
- Working with confidential data
Penetration Testing
- We are launching a new product
- A client or investor requests an audit
- We are preparing for certification
- We don't know how vulnerable we are
Protection of mobile infrastructure
- Confidential negotiations
- A public figure is at risk
- Sensitive information
- Suspicion of surveillance

Process
How is the work going?
A transparent process from the first call to the finished infrastructure
[ Step 0.1 ]
Advice
A short conversation to understand your situation: what is changing (new office, growth, preparing for certification, working with sensitive data), what is already built and where the biggest risks are. At the exit, you understand exactly what is worth checking and where to start - without obligations.
[ Step 0.2 ]
Audit and survey
We examine the network, servers, access rights, configurations and backups. We fix weak points and form a clear picture of the current state.
[ Step 0.3 ]
Plan and coordination
Based on the audit, we form a plan: what we do, in what order, at what time and within what budget. You see the full volume before launch — no surprises in the process.
[ Step 0.4 ]
Implementation
Securely agreed works: network design and configuration, server hardening, access control, reliable backup. We work step by step, with control at every step.
[ Step 0.5 ]
Check and transfer
We check that everything works as it should: we test real recovery from backups, access control and remote access. We transfer documentation and network diagrams so that your team understands how it is organized and does not depend on one person.
Cases
Results from real projects
E-commerce
[ 0.1 ]Review:
Found 47 vulnerabilities, 8 of them critical, including authorization and configuration issues
Services:
See case [+]- Cybersecurity audit
- Penetration Testing
- Infrastructure protection
- Backup
FinTech company
[ 0.2 ]Review:
Prepared the infrastructure for GDPR requirements, checked the protection of payment systems and implemented comprehensive measures to protect financial data
Services:
See case [+]- Cybersecurity audit
- Penetration Testing
- Mobile security
- Infrastructure protection
SaaS product
[ 0.3 ]Review:
Conducted web application and API testing, identified weak points in access logic and helped build system protection of cloud infrastructure
Services:
See case [+]- Cybersecurity audit
- Penetration Testing
- Mobile security
- Infrastructure protection
About Us
Cybersecurity that works
SafeNet Cyber is a Ukrainian team that builds practical cybersecurity for business. We do not blindly sell "boxed" solutions: each project begins with an infrastructure survey and risk assessment, and ends with a working security system with documentation and support.
Our task is not just to find a problem, but to show how it affects the business and what needs to be done to close it
Learn more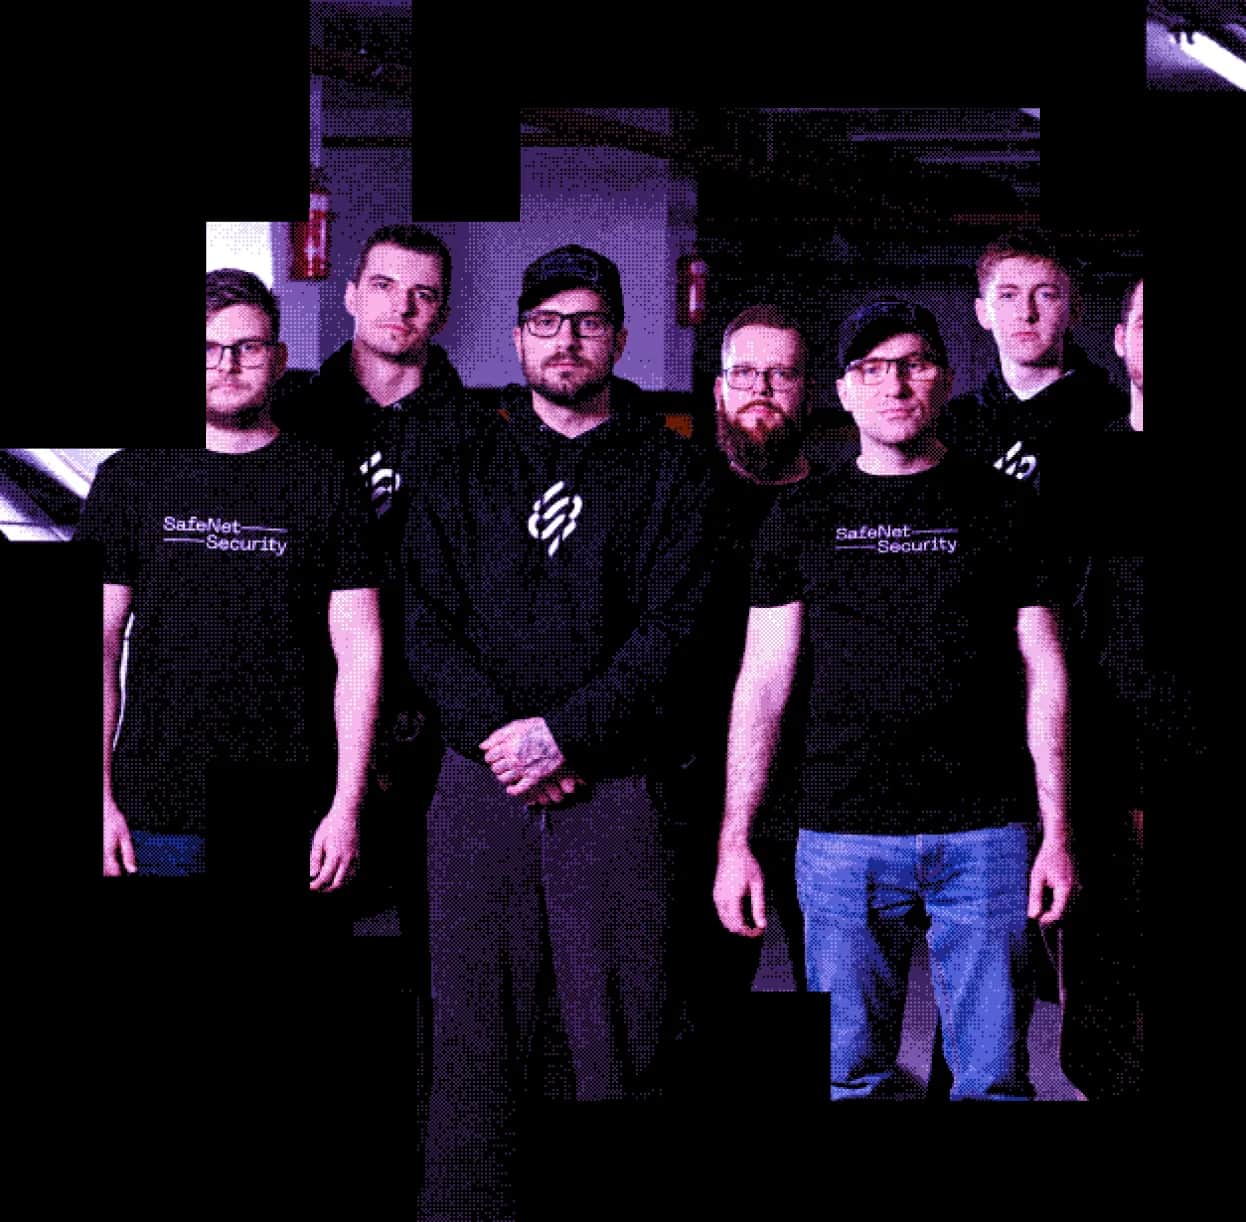
FAQ
Important questions
Check where your business could be losing data or money
A short conversation, after which you will understand exactly what should be checked and where to start
Blog
Materials that help avoid problems
Where problems most often arise in business systems
We analyze typical errors that cause companies to lose data, access to systems or control over infrastructure
Read [+]
What penetration testing shows and why a scanner is not enough
Explaining how hands-on testing helps detect real-world attack scenarios on web applications and APIs
Read [+]
How to build a secure network infrastructure for business
The basic principles of segmentation, redundancy and perimeter protection for the stable operation of the company
Read [+]
How to protect executives' smartphones and corporate communications
Practical recommendations to reduce the risk of leakage of confidential information through mobile devices
Read [+]
How to prepare your company for GDPR, ISO 27001 and other requirements
What needs to be implemented to meet security standards and pass the audit successfully
Read [+]
What to do if you suspect a cyber attack
A step-by-step action plan for incident localization, preservation of evidence and minimization of consequences
Read [+]